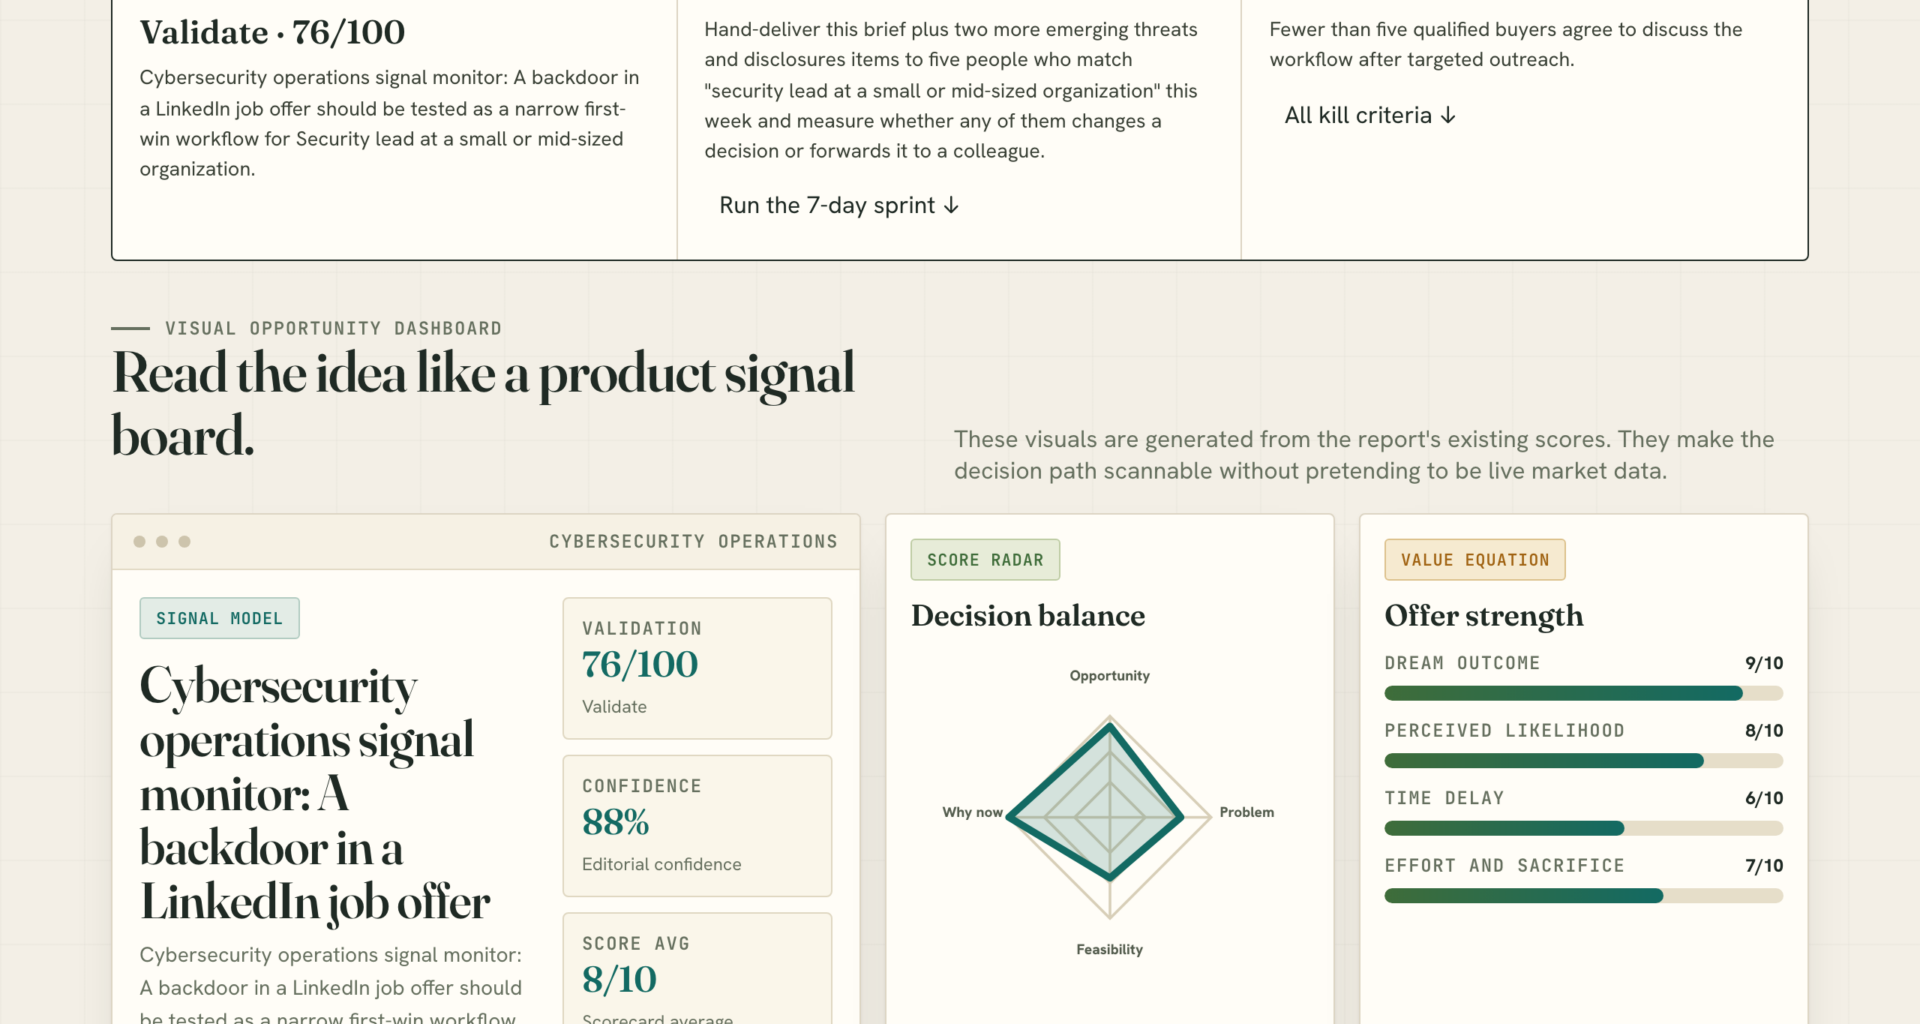
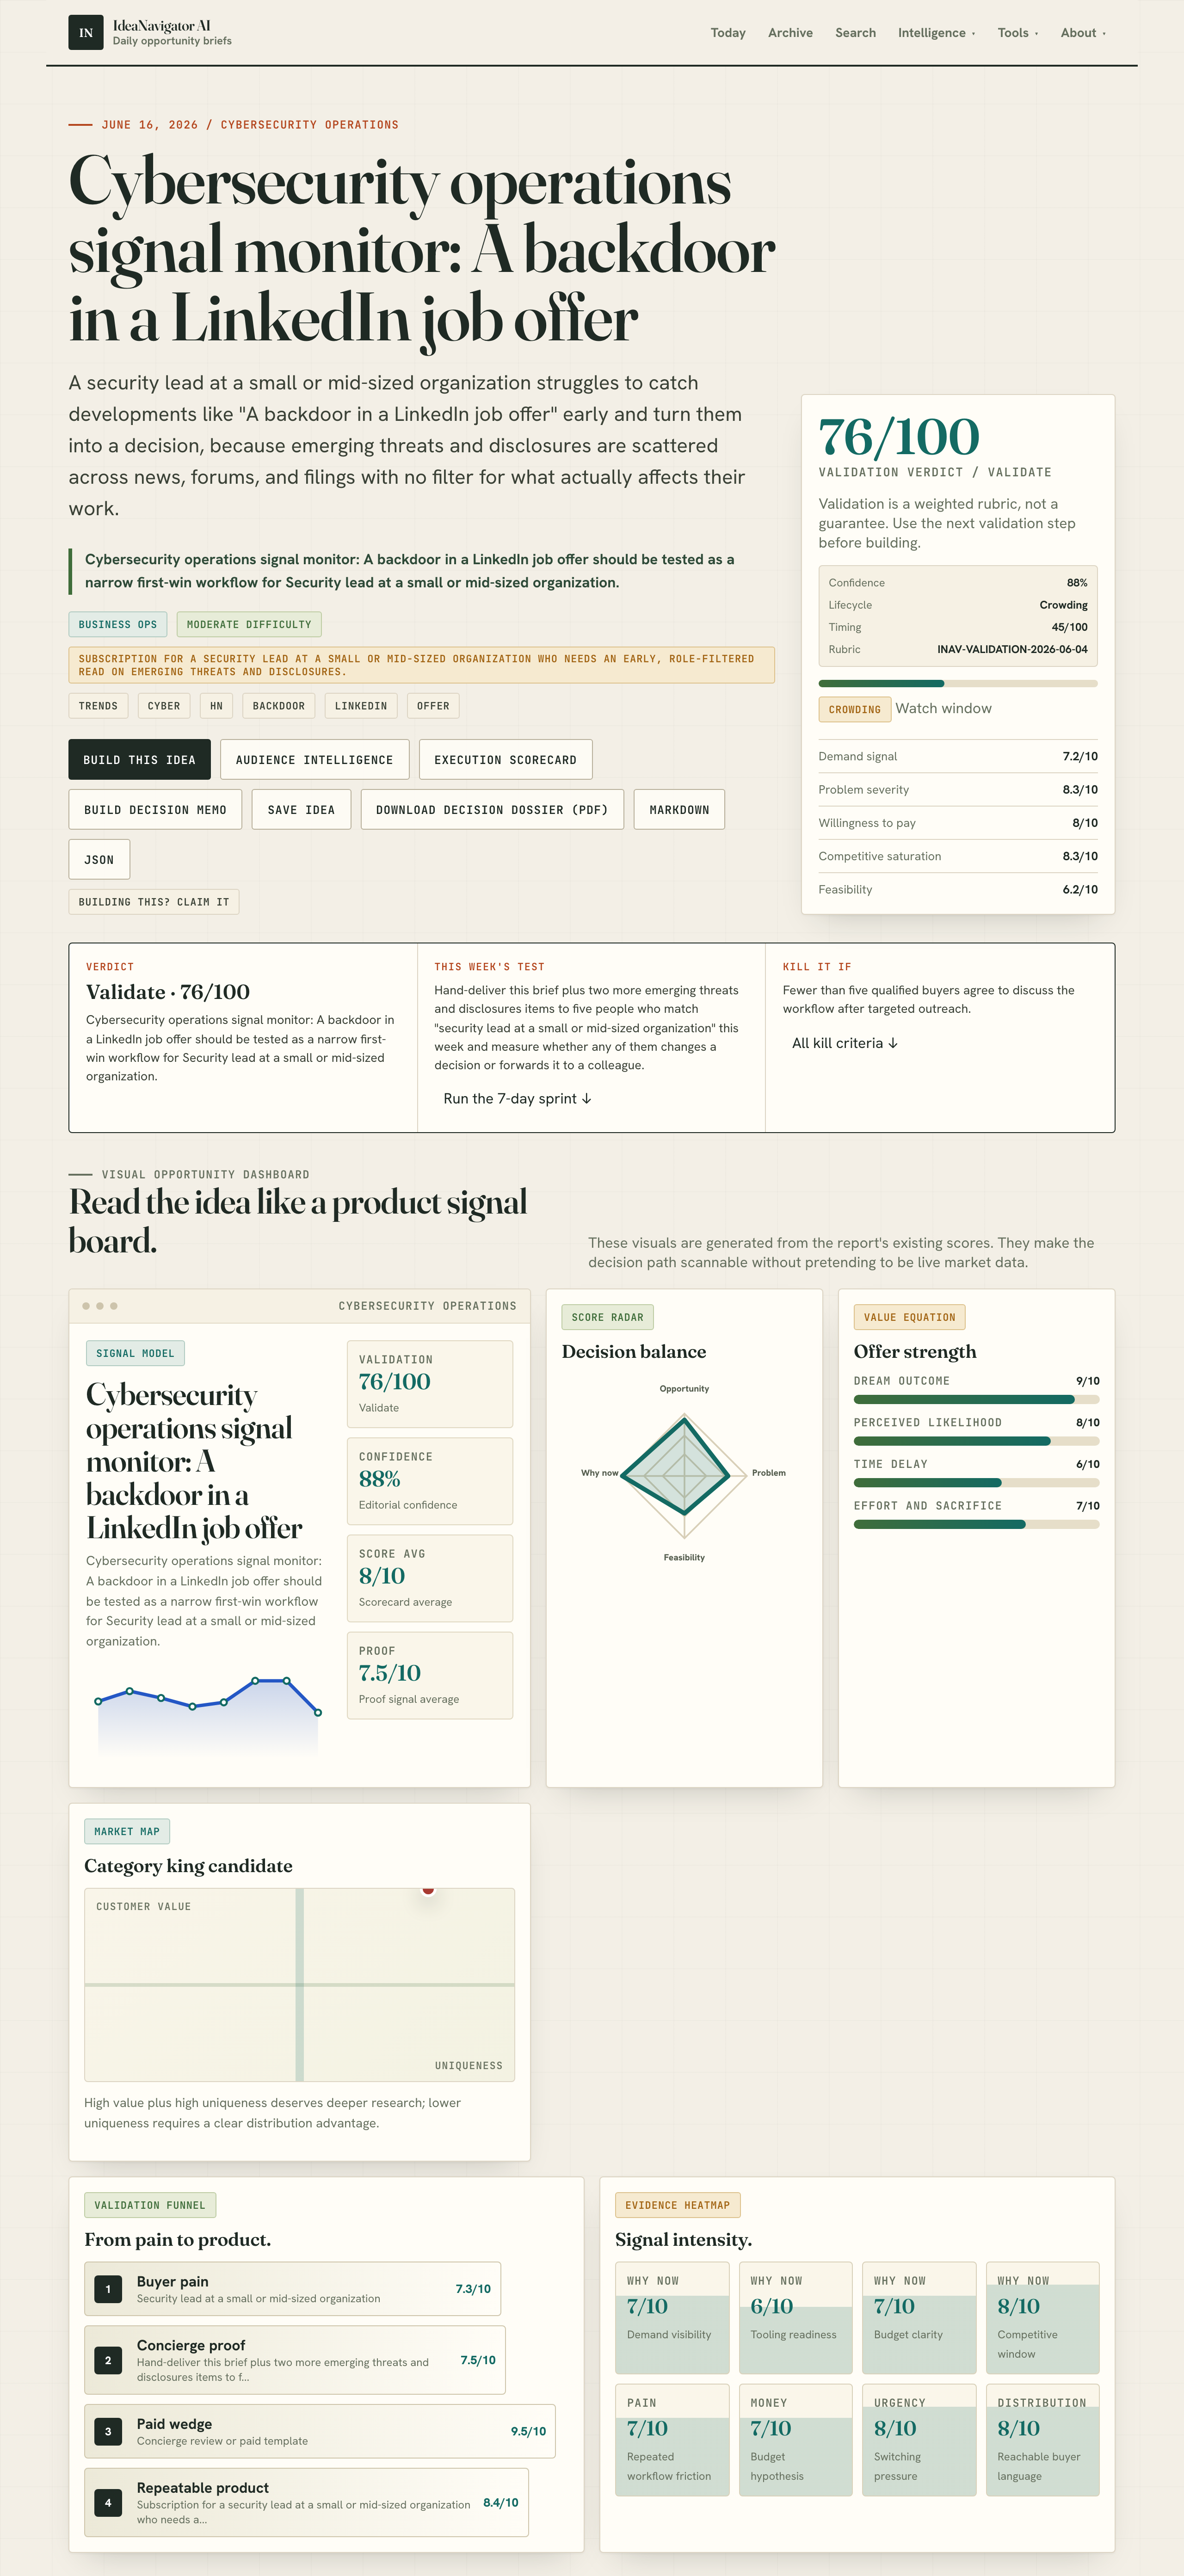
📊 Full opportunity report: Cybersecurity operations signal monitor: A backdoor in a LinkedIn job offer on IdeaNavigator AI — validation score, market gap, and execution plan.
Listen free for 30 days with Audible
Thousands of audiobooks and originals — cancel anytime.
Start your free trialAs an affiliate, we earn on qualifying purchases.
TL;DR
Cybersecurity analysts detected a backdoor embedded in a LinkedIn job offer. This development highlights emerging threats that could compromise organizational security. The discovery underscores the need for vigilant monitoring of recruitment-related communications.
Cybersecurity analysts have confirmed the detection of a backdoor embedded in a LinkedIn job offer, raising concerns over potential exploitation by malicious actors. The discovery was made during routine monitoring of emerging threat signals, emphasizing the importance of scrutinizing recruitment-related communications for security vulnerabilities.
The backdoor was identified through cybersecurity operations signal monitoring, which flagged suspicious activity associated with a specific LinkedIn job posting. The malicious code appears to be designed to provide unauthorized access to systems once the job offer is accepted or interacted with. Experts caution that such backdoors could be exploited for data theft, malware deployment, or further network infiltration.
While the exact technical details of the backdoor are still being analyzed, cybersecurity professionals emphasize that this type of threat is consistent with tactics used in targeted cyber espionage campaigns. The incident highlights the evolving landscape of social engineering and supply chain attacks, where seemingly legitimate communications are weaponized for cyber intrusions.
Implications for Corporate Security and Recruitment Processes
This discovery underscores the increasing sophistication of cyber threats targeting recruitment channels, which are often overlooked as attack vectors. Small and mid-sized organizations may be particularly vulnerable due to limited security resources. The incident demonstrates the necessity for organizations to implement rigorous vetting and monitoring of online communications, especially those related to hiring.
Understanding and detecting such threats early can prevent potential breaches, data loss, and reputational damage. It also highlights the need for cybersecurity teams to incorporate social engineering and recruitment-related signals into their threat detection strategies.
As an affiliate, we earn on qualifying purchases.
Over recent years, cybercriminals have increasingly targeted social engineering tactics, exploiting trust in professional networks like LinkedIn. Previously, malware campaigns focused on email phishing, but recent trends show a shift towards embedding malicious code within legitimate-looking offers, messages, or documents. The current detection aligns with broader patterns of exploiting online recruitment channels for cyber espionage and financial gain.
This incident is part of a broader pattern where threat actors leverage trusted platforms to infiltrate organizational networks, often before traditional security measures can detect malicious activity. The use of backdoors in social engineering campaigns has become a notable concern for cybersecurity professionals worldwide.
“The backdoor embedded in this LinkedIn job offer exemplifies how attackers are increasingly weaponizing recruitment channels to gain unauthorized access.”
— an anonymous cybersecurity researcher
network intrusion detection system
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Technical Details and Extent of the Threat Remain Unclear
It is not yet confirmed how widespread this backdoor is or whether it has been exploited in active campaigns. The technical specifics of the malicious code are still under analysis, and it remains unclear if other similar backdoors are present in online recruitment platforms.
As an affiliate, we earn on qualifying purchases.
Further Investigation and Monitoring Will Clarify Threat Scope
Cybersecurity teams are expected to continue analyzing the backdoor’s technical details and monitor for related incidents. Organizations are advised to review their recruitment communication protocols and enhance detection capabilities for social engineering threats. Updates on the threat’s scope and potential mitigation strategies are anticipated in the coming weeks.
security awareness training for employees
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
How can organizations protect themselves against backdoors in online job offers?
Organizations should implement strict vetting procedures for online communications, train staff on social engineering risks, and use threat intelligence tools to monitor for suspicious activity related to recruitment channels.
Is this backdoor linked to a specific cybercriminal group?
There is currently no confirmed attribution to any known threat actor. Investigations are ongoing to determine potential links or motives.
What should job seekers or applicants do if they encounter suspicious offers?
They should verify the authenticity of the offer through official company channels, avoid clicking on suspicious links, and report any suspicious activity to cybersecurity authorities or their organization’s security team.
Are small and mid-sized organizations more vulnerable to this type of threat?
Yes, smaller organizations often have fewer resources dedicated to cybersecurity and may be less prepared to detect sophisticated social engineering attacks, making them more vulnerable.
Source: IdeaNavigator AI
Fall yard work Picks
leaf blowers
As an affiliate, we earn on qualifying purchases.